会社でSRX100を購入したのですが、Juniper製品の設定は初めてでハマってて自宅でいろいろ試してました。
とりあえず自宅での接続は全部うまくいったので、会社用にこれから設定を変えていってみようと思います。
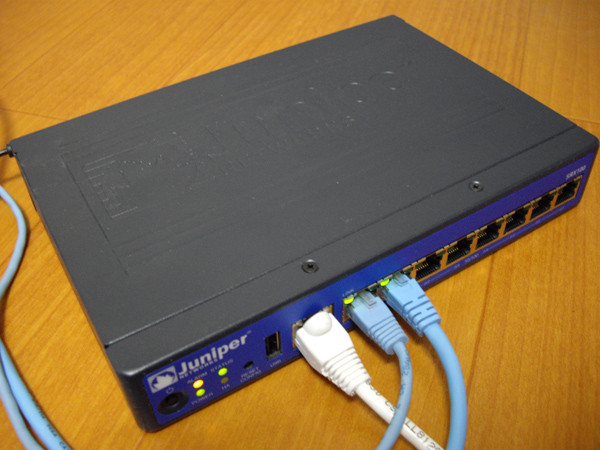
ポート0/0にONUからのLANケーブル、ポート0/1にスイッチングハブへのケーブルをつないでます。
グローバルIPアドレスあり、PPPoEでのインターネット接続。
JUNOSは10.4R1.9にアップグレード済み。
以下の設定は、セキュリティを全く考慮してないです。
root@ebisu-srx100> show configuration | no-more
## Last commit: 2011-02-11 14:10:33 JST by root
version 10.4R1.9;
system {
    host-name ebisu-srx100;
    time-zone Asia/Tokyo;
    root-authentication {
        encrypted-password "rootのパスワード"; ## SECRET-DATA
    }
    name-server {
        8.8.8.8;  ## google public dns
        8.8.4.4;
    }
    services {
        ssh;
        telnet;
        web-management {
            http {
                interface vlan.0;
            }
            https {
                system-generated-certificate;
                interface vlan.0;
            }
        }
        dhcp {
            router {
                192.168.1.1;
            }
            pool 192.168.1.1/24 {
                address-range low 192.168.1.2 high 192.168.1.145;
            }
            propagate-settings fe-0/0/1.0;
        }
    }
    ntp;
}
interfaces {
    interface-range interfaces-trust {
        member fe-0/0/1;
        member fe-0/0/2;
        member fe-0/0/3;
        member fe-0/0/4;
        member fe-0/0/5;
        member fe-0/0/6;
        member fe-0/0/7;
        unit 0 {
            family ethernet-switching {
                vlan {
                    members vlan-trust;
                }
            }
        }
    }
    fe-0/0/0 {
        unit 0 {
            encapsulation ppp-over-ether;
        }
    }
    lo0 {
        unit 0 {
            family inet {
                address 127.0.0.1/32;
            }
        }
    }
    pp0 {
        unit 0 {
            ppp-options {
                pap {
                    default-password "インターネット接続用のパスワード"; ## SECRET-DATA
                    local-name "インターネット接続用のID";
                    local-password "インターネット接続用のパスワード"; ## SECRET-DATA
                    passive;
                }
            }
            pppoe-options {
                underlying-interface fe-0/0/0.0;
                idle-timeout 0;
                auto-reconnect 120;
                client;
            }
            family inet {
                mtu 1454;
                negotiate-address;
            }
        }
    }
    vlan {
        unit 0 {
            family inet {
                address 192.168.1.1/24;
            }
        }
    }
}
routing-options {
    static {
        route 0.0.0.0/0 {
            next-hop pp0.0;
            metric 0;
        }
    }
}
security {
    nat {
        source {
            rule-set trust-to-untrust {
                from zone trust;
                to zone untrust;
                rule source-nat-rule {
                    match {
                        source-address 0.0.0.0/0;
                    }
                    then {
                        source-nat {
                            interface;
                        }
                    }
                }
            }
        }
        static {
            rule-set untrust-static-nat {
                from zone untrust;
                rule static-nat-rule {
                    match {
                        destination-address xxx.xxx.xxx.xxx/32;  ## 自宅のグローバルIP
                    }
                    then {
                        static-nat prefix 192.168.1.200/32;   ## 自宅サーバ
                    }
                }
            }
        }
    }
    zones {
        security-zone trust {
            host-inbound-traffic {
                system-services {
                    all;
                }
                protocols {
                    all;
                }
            }
            interfaces {
                vlan.0;
            }
        }
        security-zone untrust {
            host-inbound-traffic {
                system-services {
                    all;
                }
                protocols {
                    all;
                }
            }
            interfaces {
                fe-0/0/0.0;
                pp0.0;
            }
        }
    }
    policies {
        from-zone trust to-zone untrust {
            policy trust-to-untrust {
                match {
                    source-address any;
                    destination-address any;
                    application any;
                }
                then {
                    permit;
                }
            }
        }
        from-zone untrust to-zone trust {
            policy untrust-to-trust {
                match {
                    source-address any;
                    destination-address any;
                    application any;
                }
                then {
                    permit;
                }
            }
        }
    }
    flow {
        tcp-mss {
            all-tcp {
                mss 1414;
            }
        }
    }
}
vlans {
    vlan-trust {
        vlan-id 3;
        l3-interface vlan.0;
    }
}ところで内部向けのDNSをうまくできないかな。
